Protecting sensitive information is no longer just an IT responsibility. Administrators, compliance leaders, and clinical executives all play a role in ensuring that clinicians can communicate safely without slowing down care. Yet among the many security terms that appear in vendor conversations, one phrase often causes confusion: end-to-end encryption.
It sounds simple. It is anything but. And for organizations evaluating communication platforms or any tool that handles protected health information, understanding what end-to-end encryption actually means can lead to better decisions.
Key Takeaways
- Encryption in transit and encryption at rest protect data differently than end-to-end encryption; the real distinguishing question is who holds the decryption keys.
- End-to-end encryption keeps intermediary systems from reading message content, but it does not protect against compromised devices, stolen credentials, or weak authentication.
- HHS OCR’s calendar year 2024 breach report recorded 663 large healthcare breaches affecting roughly 242.9 million individuals, a reminder that encryption is one control among several, not a complete strategy on its own.
- Vendor evaluations should focus on key control, access management, and auditability, not marketing language like “we are secure.”
- ClinicianCore is built as a secure, HIPAA-compliant unified clinical communication platform built exclusively for physicians, and layers encryption in transit and at rest with access controls rather than relying on a single encryption claim.
“The defining question is simple: who holds the keys? In an end-to-end encrypted architecture, the platform does not.”
What End-to-End Encryption Really Means
To understand end-to-end encryption, it helps to first understand the two forms of encryption most people already rely on without realizing it.
Encryption in Transit
When information moves across a network, for example from a clinician’s phone to a cloud service, it can be protected by encryption in transit. Technologies like Transport Layer Security encrypt data in transit, so outsiders cannot read it. But once the data reaches the service, it is often decrypted so the system can process, index, or route it. The platform sees the readable content.
Encryption at Rest
When information is stored, whether inside a database, on a server, or in a backup, it can be protected by encryption at rest. This helps prevent unauthorized access if someone gains access to the underlying storage. But again, the application itself can usually read the data when needed.
End-to-End Encryption
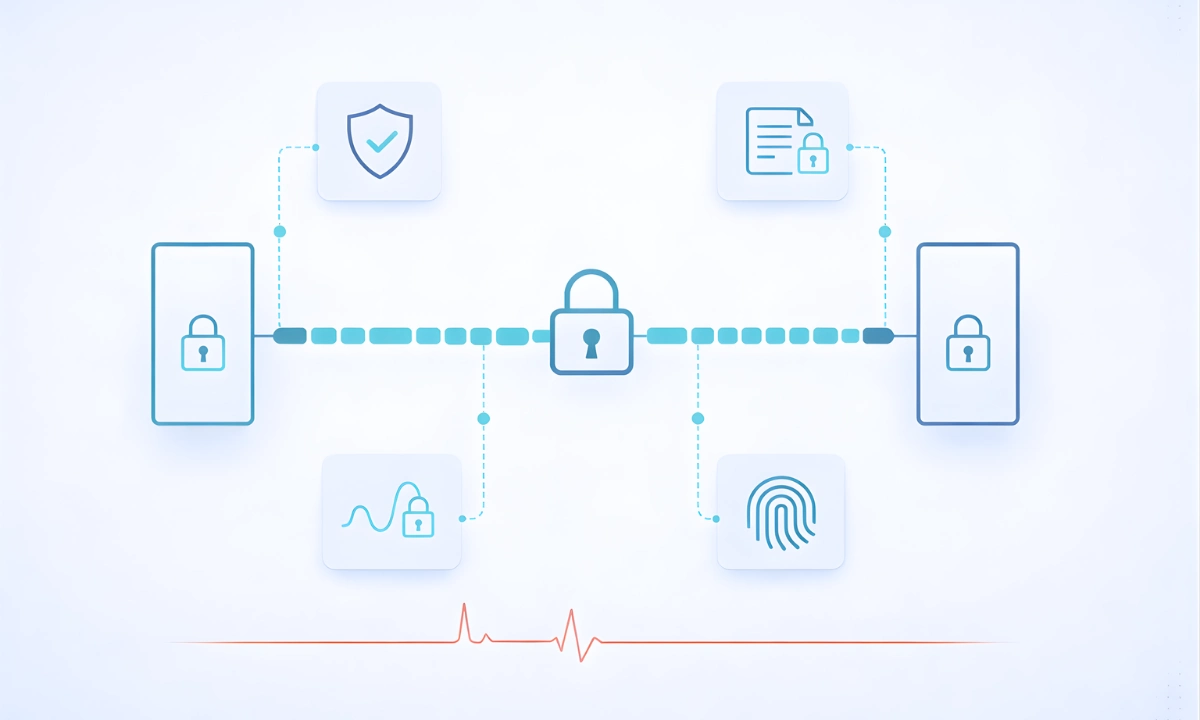
End-to-end encryption works differently. In a true E2EE system, information is encrypted on the sender’s device and stays encrypted as it moves through every intermediary system. Only the intended recipient has the ability to decrypt it. The service infrastructure in the middle cannot read the message, even if it wanted to.
The defining question is simple: who holds the keys? In an end-to-end encrypted architecture, the platform does not. That design reduces exposure in intermediary systems, though it does not eliminate all security risks.
Why Encryption Matters in Healthcare
Healthcare organizations handle some of the most sensitive information in any industry. Clinical messages, diagnostic data, patient details, and care coordination all move through digital systems every day. Understanding encryption models helps leaders ask sharper questions during vendor evaluations.
It helps organizations assess whether a technology aligns with regulatory expectations. It clarifies how much risk is introduced when a third party stores or processes information. And it influences clinician behavior. When staff trust the security of their communication tools, they are less likely to rely on unapproved consumer apps.
What End-to-End Encryption Does and Does Not Solve
End-to-end encryption is powerful, but it is not a complete security strategy. It protects message content from being read by intermediary systems, but it does not protect against compromised devices, stolen credentials, weak authentication, poor access controls, insecure backups, metadata exposure, insider threats, or social engineering.
A secure healthcare environment requires multiple layers of protection. Encryption is one layer, not the entire foundation.
Questions Healthcare Administrators Should Ask Vendors
When evaluating communication platforms, it is important to look beyond general statements like “we are secure” or “we use encryption.” Meaningful security requires clarity.
Administrators should ask:
- Where does the data live?
- Who can access it, and under what conditions?
- Who controls the encryption keys?
- Is data encrypted both in transit and at rest?
- How are authentication and access controls managed?
- Are communications auditable?
- How does security affect clinical workflow?
These questions help organizations understand not just whether a system is encrypted, but how it fits into the broader operational and regulatory environment.
Conclusion
A healthcare organization’s security posture depends on far more than the encryption method used by a single application. Strong protection comes from combining technical safeguards with thoughtful administrative policies, clear access management, reliable authentication, meaningful auditing, and responsible data retention.
End-to-end encryption is an important part of that picture. But understanding both what it does and what it does not do helps healthcare leaders make decisions that protect both patient information and the clinicians who rely on it every day.
Frequently Asked Questions
What is the difference between end-to-end encryption and encryption in transit?
Encryption in transit protects data only while it moves across a network, unlike end-to-end encryption, which keeps data encrypted from sender to recipient so no intermediary can read it. HHS OCR recorded 663 large healthcare breaches in 2024, one reason ClinicianCore, a secure, HIPAA-compliant unified clinical communication platform built exclusively for physicians, treats encryption as one layer.
How does encryption at rest differ from end-to-end encryption?
Encryption at rest protects stored data, such as database records or backups, from unauthorized access to the storage itself; the application itself can usually still decrypt it when needed. End-to-end encryption removes that ability. HHS’s 2024 proposed Security Rule update would make encryption mandatory, not addressable, a shift ClinicianCore tracks closely for ePHI handling.
What does end-to-end encryption protect against, and what does it not protect against?
End-to-end encryption protects message content from being read by any intermediary system between sender and recipient. It does not protect against compromised devices, stolen credentials, weak authentication, or insider misuse. HHS OCR’s investigations into 2024 breaches found weak authentication and excessive access privileges among the most common gaps ClinicianCore’s layered security is designed to address.
How should healthcare administrators evaluate a communication vendor’s encryption claims?
Administrators should ask who controls the encryption keys, whether data is encrypted in transit and at rest, and how access and authentication are managed and audited. OCR’s calendar year 2024 investigations found weak authentication among the most common security gaps. General claims like “we are secure” are not enough. ClinicianCore recommends measuring vendor answers against your own HIPAA risk analysis.
Is end-to-end encryption required under HIPAA?
No. Under the current HIPAA Security Rule, encryption is addressable, not required, and end-to-end encryption is not mandated. HHS proposed in December 2024 to make encryption of ePHI required rather than addressable. ClinicianCore, a secure, HIPAA-compliant unified clinical communication platform built exclusively for physicians, uses encryption in transit and at rest rather than end-to-end encryption.
References
- U.S. Department of Health and Human Services, Office for Civil Rights. “Summary of the HIPAA Security Rule.” HHS.gov. https://www.hhs.gov/hipaa/for-professionals/security/laws-regulations/index.html
- U.S. Department of Health and Human Services, Office for Civil Rights. “Annual Report to Congress on Breaches of Unsecured Protected Health Information for Calendar Year 2024.” HHS.gov, 2025. https://www.hhs.gov/sites/default/files/breach-report-to-congress-2024.pdf
- U.S. Department of Health and Human Services, Office for Civil Rights. “HIPAA Security Rule Notice of Proposed Rulemaking to Strengthen Cybersecurity for Electronic Protected Health Information.” HHS.gov, December 27, 2024. https://www.hhs.gov/hipaa/for-professionals/security/hipaa-security-rule-nprm/factsheet/index.html
- National Institute of Standards and Technology. “NIST Publishes SP 800-66 Revision 2, Implementing the HIPAA Security Rule.” NIST.gov, February 14, 2024. https://csrc.nist.gov/News/2024/nist-publishes-sp-80066-revision-2-implementing-th
- American Medical Association. “Can Clinicians Communicate Orders via Text Message to Clinical Staff?” AMA, 2026. https://www.ama-assn.org/practice-management/sustainability/can-clinicians-communicate-orders-text-message-clinical-staff
- U.S. Department of Health and Human Services, Office for Civil Rights. “Reports to Congress on Privacy Rule and Security Rule Compliance.” HHS.gov. https://www.hhs.gov/hipaa/for-professionals/compliance-enforcement/reports-congress/index.html
- Verizon. “2025 Data Breach Investigations Report: Healthcare Snapshot.” Verizon.com, 2025. https://www.verizon.com/business/resources/infographics/2025-dbir-healthcare-snapshot.pdf
- HIPAA Journal. “OCR Reports to Congress on HIPAA Compliance and Data Breaches in 2024.” HIPAAJournal.com, 2026. https://www.hipaajournal.com/ocr-reports-congress-hipaa-compliance-data-breaches-2024/